Security Audits Built to Find
Real Risk
Penetration testing, audits, and hardening across web apps, mobile apps, APIs, and cloud infrastructure — grounded in real attack patterns, not a compliance checklist.
One engineering team.
Working across your timezone.
AxioNet is remote-first by design. With weekly async standups, dedicated project managers, and shared real-time dashboards, distance never means losing visibility over your project.


Ready to accelerate your growth?
Let's discuss how our Cybersecurity expertise can help you scale faster and build better.
Start your project todayCybersecurity, delivered end to end.
Penetration Testing
Manual and automated testing of your web apps, mobile apps, and APIs to find vulnerabilities before attackers do.
Security Audits
Comprehensive reviews of your codebase, infrastructure, and access controls.
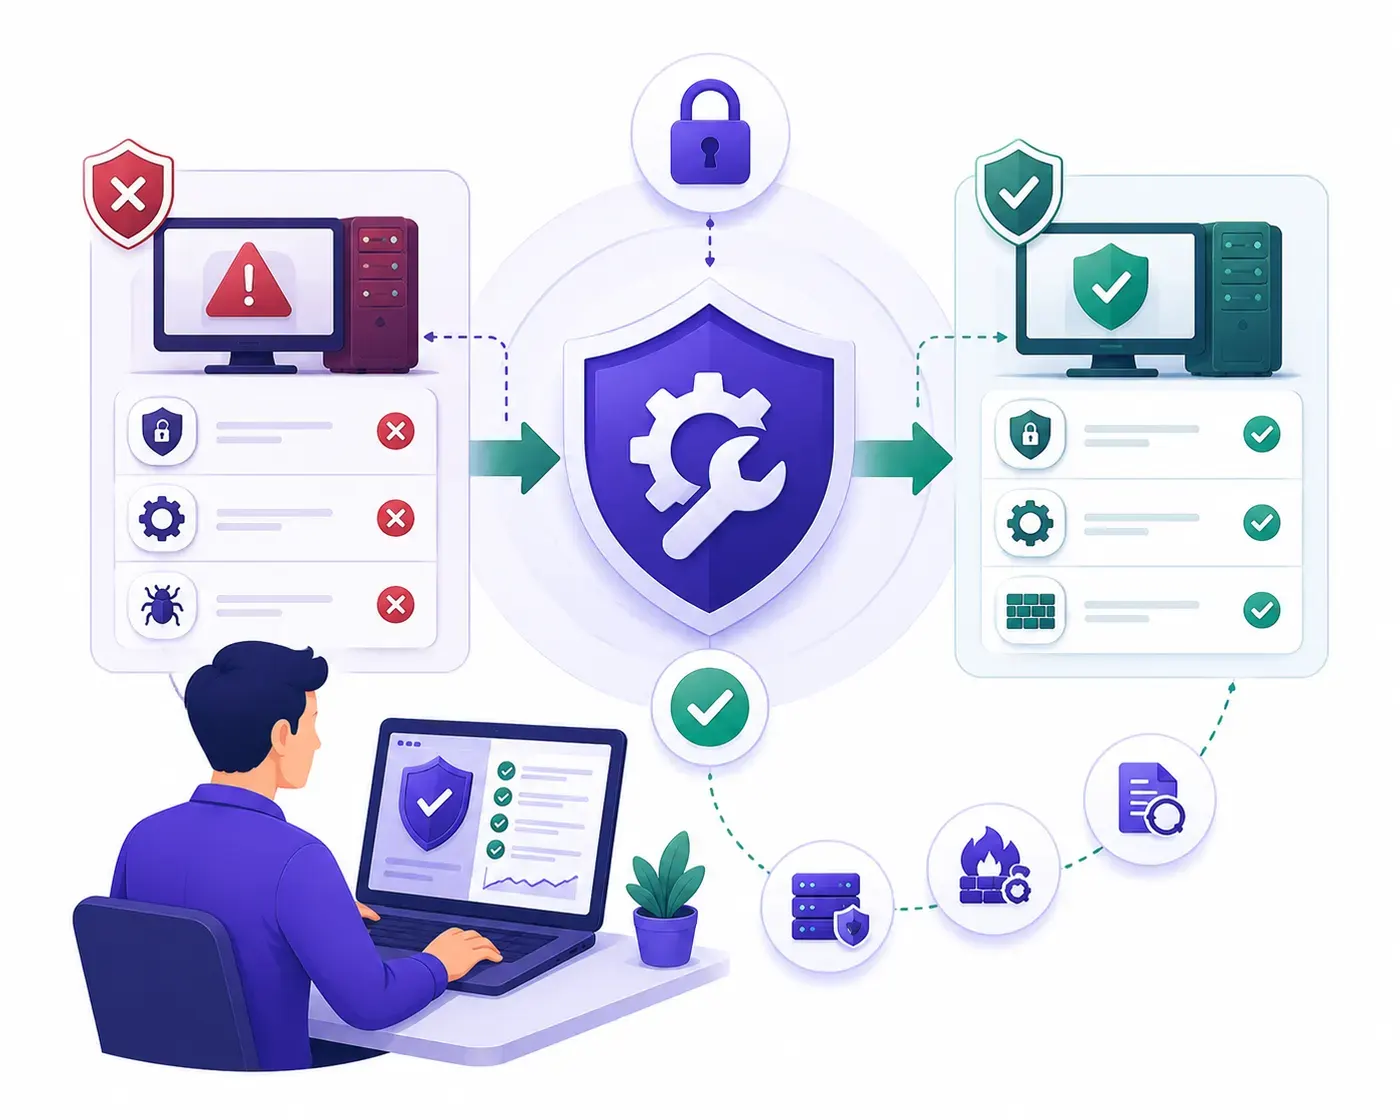
Hardening & Remediation
We don't just report issues — we patch and secure the vulnerabilities we find.
Continuous Monitoring
Real-time alerting for unauthorized access or unusual activity.
Compliance Readiness
Preparing your infrastructure for SOC2, HIPAA, or GDPR compliance audits.
Zero-Trust Architecture
Designing access controls where every internal and external request is verified.
Powered by the Best.
Industry-leading technologies powering enterprise-grade solutions.
METHODOLOGY
The Process
Discovery
Understanding your brand goal.
Deep dive into your business objectives, target audience, competitive landscape, and technical constraints to establish a bulletproof roadmap.
Architecture
Planning the tech stack.
Designing cloud infrastructure, data schemas, security protocols, and component hierarchies for effortless long-term scalability.
Development
Clean, rigorous coding.
Writing modular, type-safe, Core Web Vitals optimized code with continuous integration and weekly staging server deployments.
Launch & Scale
Deployment & continuous optimization.
Zero-downtime production deployment, 24/7 automated threat monitoring, performance auditing, and ongoing feature iteration.
Related services
Pairs well with cybersecurity.
FAQ
Common questions.
How often should we run a security audit?
At minimum annually, and after any major release or infrastructure change — attack surfaces shift every time your system changes.
Do you provide a report we can share with clients/compliance?
Yes, every engagement includes a detailed findings report suitable for internal review or compliance requirements.
Will testing disrupt our live systems?
We scope testing windows and methods to avoid disrupting production, and coordinate timing with your team in advance.
Let's build
Book a strategy call.
Walk away with a clear roadmap.
Tell us where you are and where you want to be. In one call we'll map the architecture, the timeline, and the investment — then send a fixed-scope proposal within 48 hours.